

Artificial intelligence is becoming deeply embedded in modern businesses. Enterprises are using AI to analyse data, automate workflows, support employees, improve customer experiences, and make important business decisions.
As AI adoption expands, security teams face a new challenge. Traditional cybersecurity controls are still essential, but they do not address every risk created by AI.
AI systems can process sensitive information, interact with external services, generate unpredictable outputs, and increasingly perform actions without direct human intervention. These capabilities create new risks that require organizations to rethink how AI is managed.
This is why AI governance is becoming an important part of enterprise security.
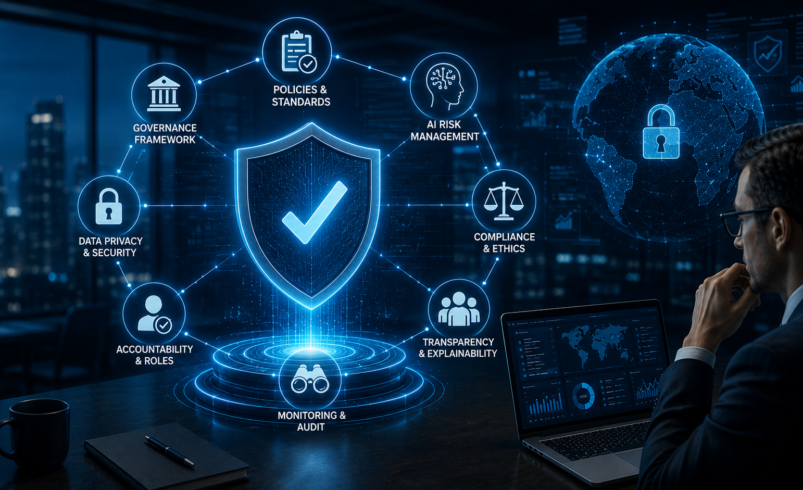
AI governance provides the policies, processes, responsibilities, and controls organizations need to manage AI throughout its lifecycle. When implemented effectively, it connects AI adoption with security, privacy, compliance, and business accountability.
What Is AI Governance?
AI governance is the framework an organization uses to manage how artificial intelligence is developed, purchased, deployed, monitored, and retired.
It defines who is responsible for AI systems and establishes expectations around data usage, security, privacy, risk management, transparency, and human oversight.
Governance is not simply about creating an AI policy and asking employees to follow it.
Effective governance connects policies to practical controls and workflows.
For example, when a business wants to introduce a new AI application, governance can determine which data the application will access, what risks need to be assessed, who should approve it, and what monitoring should continue after deployment.
This creates a more structured approach to enterprise AI adoption.
Why AI Governance Has Become a Security Issue
AI changes the way organizations interact with data.
Employees can enter information into AI assistants, applications can send data to external models, and AI agents can retrieve information from internal systems.
This creates new data flows that security teams need to understand.
An organization may have strong network security and identity management but still face significant AI-related risk if employees unknowingly send confidential information to an unapproved AI service.
Similarly, an AI agent with excessive permissions could access information or perform actions beyond its intended purpose.
AI governance helps security teams address these risks before they become incidents.
AI Governance and Enterprise Data Protection
Enterprise data is one of the biggest concerns surrounding AI adoption.
Businesses process customer records, financial information, intellectual property, employee data, contracts, source code, and other confidential information.
Not every AI application should have access to this information.
AI governance can establish rules that determine what categories of data may be processed by specific AI systems.
Data classification can help organizations identify sensitive information before it enters an AI workflow. Additional controls such as anonymization, masking, encryption, and access restrictions can reduce unnecessary exposure.
The objective is simple: AI should have access to the information it needs, but not everything an organization possesses.
Managing Shadow AI
Shadow AI has become a major governance challenge.
Employees can easily discover and start using AI tools without going through traditional IT procurement processes. These tools may provide real productivity benefits, but they can also create unknown data flows.
An employee might upload a confidential document to an external AI service simply because it provides a convenient way to summarize the content.
Security teams may have no visibility into that activity.
A strong AI governance program should therefore make approved AI tools easy to access and use.
Organizations should combine clear policies with practical security controls and employee education.
Simply banning AI tools may encourage employees to find less visible alternatives.
AI Governance and Access Control
AI systems should operate under clearly defined permissions.
This becomes particularly important as businesses deploy AI agents capable of interacting with enterprise applications.
An AI agent that helps employees search internal documents may need access to a knowledge base, but it should not automatically receive access to payroll systems, legal records, or financial databases.
The principle of least privilege should apply to AI just as it does to users and applications.
Organizations should regularly review AI permissions to ensure that access remains appropriate as systems and business requirements change.
Protecting AI From Prompt Injection
AI governance also needs to address threats that are specific to AI systems.
Prompt injection is one example.
An attacker may place malicious instructions inside a document, email, webpage, or other data source that an AI system processes. If the system interprets that content as a trusted instruction, it may behave in an unexpected way.
The risk becomes more serious when an AI system can access enterprise applications or take autonomous actions.
Organizations should therefore include AI security testing in their governance process.
Before deployment, AI applications should be tested against malicious inputs, unexpected instructions, unauthorized data requests, and other relevant attack scenarios.
Continuous AI Monitoring
AI governance should continue after an application is deployed.
AI systems can change over time. Models can be updated, new integrations can be added, employees can modify workflows, and the types of information processed by an AI system can evolve.
A system that was considered low-risk when it was first approved may become more important or more exposed later.
Continuous monitoring helps organizations identify changes in AI usage, data access, system behaviour, and security risks.
Audit logs can also help security and compliance teams understand what happened during an incident.
This makes monitoring an important component of long-term AI governance.
Human Oversight and AI Security
Not every AI decision should be completely autonomous.
Human oversight becomes particularly important when AI systems influence decisions with significant financial, legal, operational, or customer consequences.
Organizations can establish risk-based approval requirements.
A low-risk AI assistant may be allowed to generate internal summaries automatically, while an AI system making recommendations related to financial transactions may require human approval.
The purpose is not to eliminate automation.
Instead, human oversight creates a layer of accountability around decisions where mistakes could have serious consequences.
AI Governance and Compliance
AI governance also supports regulatory and compliance requirements.
Depending on the organization’s location and industry, frameworks and regulations such as GDPR, the EU AI Act, NIST AI Risk Management Framework, and ISO/IEC 42001 may influence how AI systems are managed.
Organizations need to understand which requirements apply to their specific AI use cases.
Governance helps create documentation around AI ownership, risk assessments, controls, approvals, monitoring, and reviews.
This documentation can become valuable evidence during audits and compliance assessments.
However, governance software or documentation alone does not guarantee compliance.
Organizations still need effective controls and responsible decision-making.
The Role of Privacy in AI Governance
Privacy should be built into AI governance from the beginning.
When AI systems process sensitive information, organizations should consider whether all of that information is actually necessary.
Data minimization can reduce exposure by limiting the information provided to an AI model.
Anonymization can provide another layer of protection by removing personally identifiable information before processing.
For organizations working with highly sensitive business data, privacy-first AI architecture can reduce risk while still allowing employees to use AI for legitimate business purposes.
How Questa AI Supports AI Governance
Questa AI takes a privacy-first approach to enterprise AI, helping organizations address data protection as part of their broader AI strategy.
Its platform focuses on protecting sensitive information during AI workflows through secure data processing and anonymization capabilities.
For enterprises concerned about confidential information reaching AI models, these controls can help reduce unnecessary exposure.
Questa AI can therefore complement an organization’s broader AI governance framework by providing a technical layer focused on privacy and secure data processing.
Governance establishes the rules, while technology helps enforce those rules within real-world AI workflows.
Building an AI Governance Framework
A practical AI governance strategy should begin with visibility.
Organizations need to know which AI applications and agents are being used across departments.
They should then evaluate the purpose of each system, the data it processes, the systems it connects to, and the potential consequences of failure.
Clear ownership should be established for important AI systems.
Security, privacy, legal, compliance, IT, and business teams should also have defined responsibilities.
As AI systems evolve, organizations should regularly review their risk classifications, permissions, vendors, and controls.
This creates a governance process that can scale alongside AI adoption.
Why Businesses Should Start Now
AI adoption is moving quickly.
Organizations that wait until AI becomes deeply embedded in their operations may find it difficult to establish governance retroactively.
Employees may already be using unauthorized tools. Sensitive information may already be moving through external AI services. AI applications may already have access to internal systems without sufficient monitoring.
Starting with governance early allows businesses to establish clear boundaries before AI adoption becomes difficult to control.
The goal is not to slow innovation.
It is to create the security foundation that allows innovation to continue safely.
Preparing for Autonomous Enterprise AI
The next stage of AI adoption will involve increasingly autonomous systems.
AI agents may retrieve information, interact with applications, make recommendations, and complete multi-step workflows.
As autonomy increases, governance becomes even more important.
Organizations will need to understand what agents can access, which actions they can perform, how those actions are monitored, and when human approval is required.
Businesses that establish strong governance today will be better prepared for this transition.
Conclusion
AI is creating new opportunities for enterprise productivity, but it is also changing the organization’s security landscape.
AI governance helps businesses manage these changes by establishing clear responsibilities, access controls, privacy requirements, monitoring processes, risk assessments, and human oversight.
Security should not be treated as something added after an AI system is deployed. It should be part of the governance framework from the beginning.
With privacy-focused solutions such as Questa AI, organizations can strengthen protection for sensitive information while building a more responsible approach to enterprise AI.
The future of secure AI adoption will depend on more than powerful models. It will depend on whether organizations can establish meaningful governance, maintain visibility, and keep control over how AI interacts with business data.